Regulation · explainer

CER and NIS2: the 24-hour clock, and what has to be ready when it starts.

Two EU directives now set the pace for how critical entities report a serious incident. The first notice is due within a day. Here is what each one asks, and what an operator needs on one record before the clock starts.

Mi-C3October 20266 min read

Two directives, one operator

The Critical Entities Resilience Directive, Directive (EU) 2022/2557 (CER), covers physical, all-hazards resilience: storms, floods, sabotage and the failure of a supplier. The NIS2 Directive, Directive (EU) 2022/2555, covers cybersecurity. They were written separately, but they meet in the same control room. Under NIS2, an entity identified as critical under CER is automatically an essential entity (NIS2, Article 3).

Member States had to identify their critical entities by 17 July 2026. For many operators of energy, water, transport and telecoms networks, that means both directives now apply to the same people, the same assets and the same incidents.

What the clocks ask

Both directives start a clock when a significant incident happens. The first step is due within a day under each of them.

DirectiveWithin 24 hoursWithin 72 hoursWithin one month
CER · Article 15Initial notificationNo separate stepDetailed report
NIS2 · Article 23Early warningIncident notificationFinal report

Nine months to the risk assessment

CER also sets a clock that starts with notification, not with an incident. A critical entity must complete its own risk assessment within nine months of being notified (Article 12), and the obligations in Chapter III apply ten months after notification (Article 6(3)). For entities notified in mid-2026, that lands around the second quarter of 2027, depending on the Member State.

What has to be ready when the clock starts

Twenty-four hours is not long. The first notice is easier to write, and the full report easier to defend, when the facts already sit together: which service was affected, how many people, which assets, what was done and who approved it. In most operations those facts live in different places: the control room, the map, the work-order system and the contact centre.

The record that supports the notification should be built while the incident unfolds, not pieced together afterwards.
  1. An amber wind warning: a storm is coming in off the sea.
  2. Power line 31 trips, and 3,410 homes and businesses lose power.
  3. Then the chain: the pump station stops, the reservoir starts to fall, the hospital and its cell site go to backup.
  4. The cell site that serves the hospital runs out first, in 4 hours.
  5. The surge floods the coast road, so the crew takes the inland road. A generator and a message to the telecoms operator go out from the same record in Affectli.

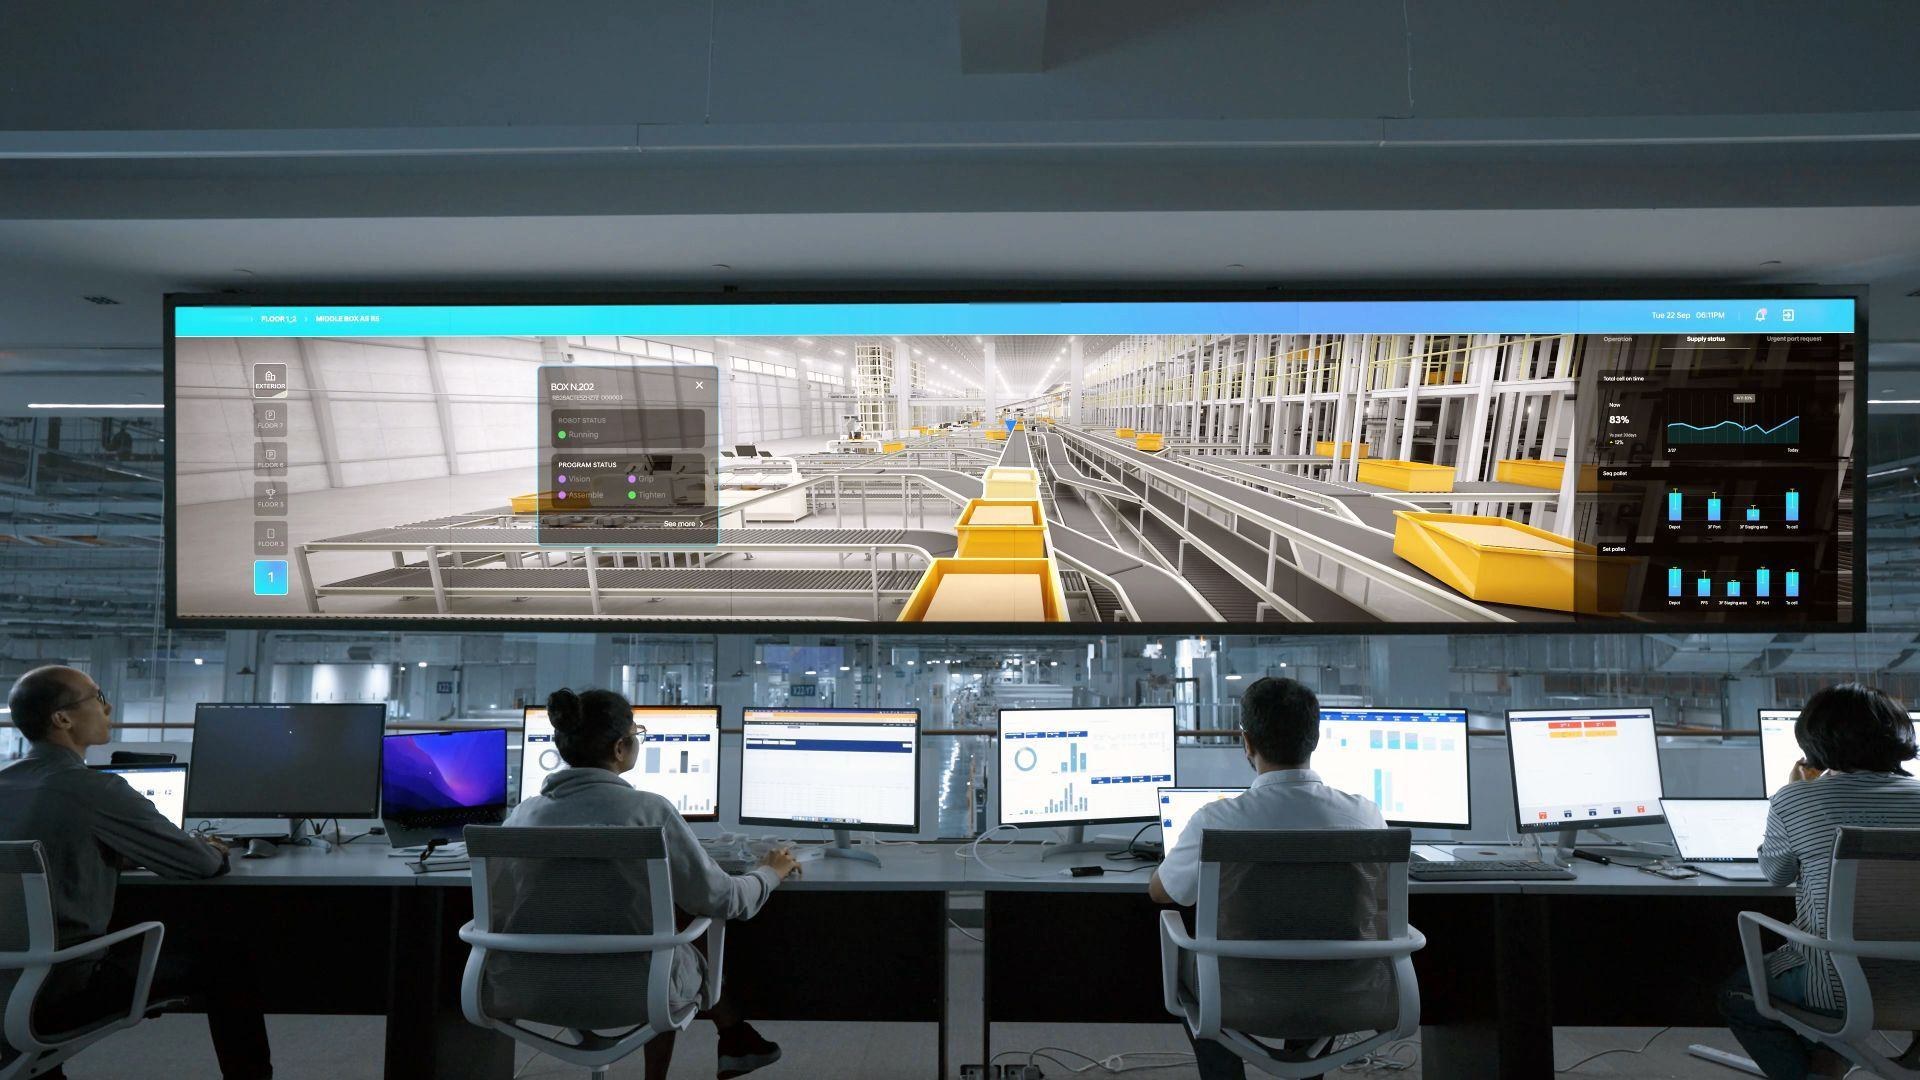
Affectli, built by Mi-C3, joins those systems into one live model of the operation. Every signal, decision and action is time-stamped and attributable, so the facts a notification needs are already on one record: the services affected, the people affected, the assets, the actions taken and the approvals.

Who answers for it

NIS2 makes cyber risk a matter for the board. Management bodies approve and oversee the risk measures and can be held liable (Article 20). For essential entities, Member States must set maximum fines of no less than €10 million or 2% of worldwide annual turnover, whichever is higher (Article 34).

Five questions for your control room this quarter

  1. If a power line trips tonight, how long does it take to list the services and the people affected?
  2. Can you show which other sectors depend on that asset, such as water, health and telecoms?
  3. Is every action during an incident recorded with a time and a name?
  4. Who drafts the 24-hour notice, and from which system do they take the facts?
  5. When did you last rehearse the one-month report from a real incident record?

Sources

  • Directive (EU) 2022/2557 on the resilience of critical entities (CER): Articles 6, 12 and 15. EUR-Lex
  • Directive (EU) 2022/2555 on measures for a high common level of cybersecurity (NIS2): Articles 3, 20, 23 and 34. EUR-Lex

See your incident record before the clock starts.

Bring one real incident. We will show you the record Affectli builds from the systems you already run.